How To Avoid the Cost and Risks of Cybersecurity in the Age of AI
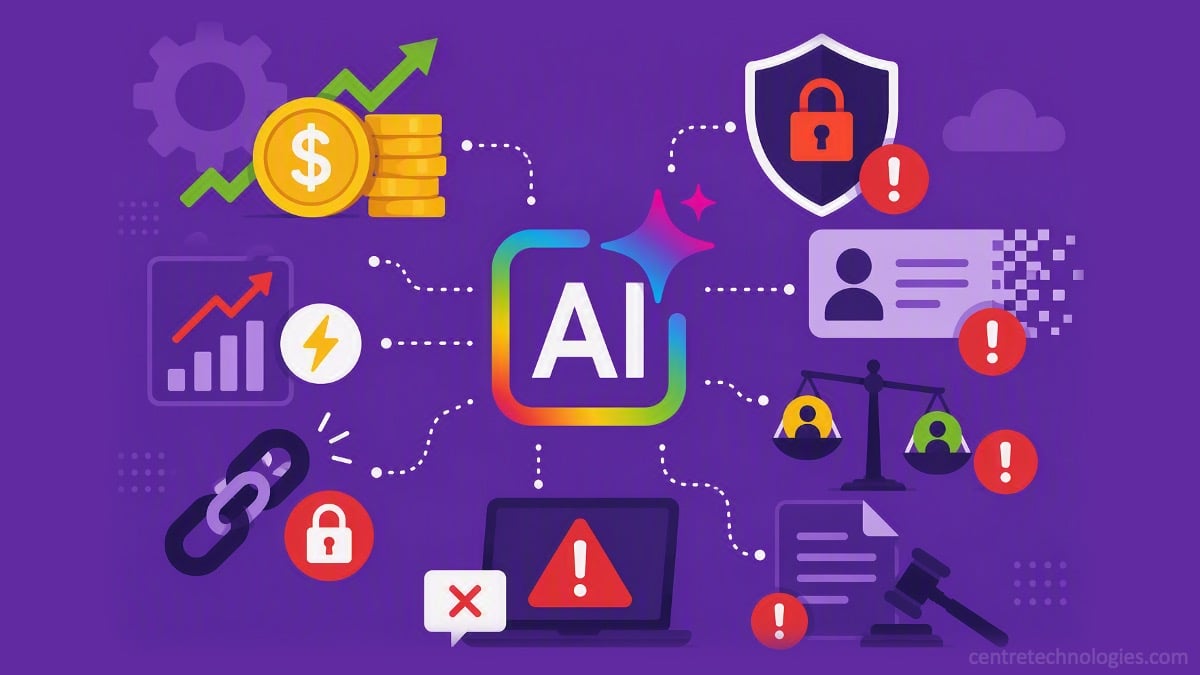
AI is helping businesses move faster than ever. It's also helping criminals attack faster than ever. Today's attackers don't need to guess who works at your company or what they do. They can scrape your website, your LinkedIn page, or old webinar recordings in minutes, then use that information to build a phishing email or even a fake video call that looks and sounds real. The good news is that businesses who build strong security habits and understand how cyber insurance actually works can lower their risk and bounce back faster when something does happen.
Featured in this article:
- AI is Continuing to Raise Ransomware Sophistication
- How to Avoid the Risks of Cyber Security Tip #1: Insurance Options
- How to Avoid the Risks of Cyber Security Tip #2: Choosing the Right Provider
- Real-Life Healthcare Cybersecurity Insurance Non-Compliance Example
- 4 Tips for to Finding the Right Cyber Insurance Fit For Your Industry
Ransomware Continues to Be the Most Common Type of Cyber Threat
Somewhere online right now, an attacker could be studying your company. AI tools can map out who handles your invoices. They can figure out which executive's voice is easy to find online. They can write a message that sounds exactly like something a real coworker or vendor would send. The attacker simply needs the right AI tool and a few minutes of your team's trust.
The unnerving part is it's already happening. AI-generated phishing emails get clicked at a rate of about 54%, which is close to what a skilled human scammer used to pull off, and far above the roughly 12% click rate of old-style generic scams. Voice cloning has gotten so fast that a criminal only needs a few seconds of audio to convincingly fake someone's voice. Deepfake video has followed the same path. There have been real cases of finance employees joining a video call where every face on the screen, including the "CFO," was fake, and still approving a large transfer because everything looked and sounded normal.
Ransomware itself has changed too. Attackers now steal your data first, then encrypt it, so even a business with solid backups still faces the threat of stolen information getting leaked publicly. Now you're thinking about the legal and financial stakes of every attack.
Here's a breakdown of what happens during a phishing style ransomware attack (the most common, by the way):
- Phishing emails deliver ransomware by hiding a harmful attachment inside a message that looks like it came from someone you trust.
- Once an employee opens that file, the infected system quietly reaches out to a server the attacker controls. That server can update the malware's instructions at any time.
-
Attackers don't always strike right away. They can sit inside a network for months before they act, which gives them time to find your most valuable data and time the attack for maximum damage.
How to Avoid the Risks of Cybersecurity
Insurance Options
Cyber insurance won't stop an attack. But it can help your business recover financially after one hits. Companies in regulated industries, or ones with a contract that requires it, should seriously consider a policy. If your business handles Personally Identifiable Information (PII) or Protected Health Information (PHI), coverage matters even more, since a convincing AI phishing email or a faked-voice phone call can trigger the same kind of loss as a full-blown breach.
Most cyber insurance policies cover first-party breach costs like:
- Legal expenses
- Forensic investigation
- Breach notification
- Credit monitoring
- Business interruption
- Data restoration
- Extortion
- Telecom fraud
- Social engineering fraud
Price shouldn't be the only thing you compare, though. The deductible matters. The coverage limits matter. So does the waiting period before your policy actually kicks in. A cheap premium that won't pay out when you need it isn't a good deal. In fact, it's a risk hiding behind a low sticker price.
Buyers Beware! Choose the Right Insurance Provider
Not getting paid is one of the most common problems businesses run into after filing a cyber insurance claim. Unfortunately, it's a noncompliance issue more often than not. Insurers want proof today, not just promises, and they're looking a lot harder at how companies actually use AI before they'll agree to pay a claim.
Cyber Insurance payouts and trends in 2026-2027 have changed because of AI.
- The old habit of checking a box that says "yes, we have security" is fading fast.
Some insurers now track live signals from a business's network instead of relying on a form filled out once a year. A few can review hundreds of individual risk signals and turn around a quote in minutes, because their systems are watching things like email security, patching habits, and exposure through outside vendors in real time. - AI has become one of the biggest new questions on the underwriting form.
Insurers want to know whether AI tools employees use day to day are approved and whether anyone reviews what employees type into them. They're also starting to ask how much a company's AI systems run on their own without a person checking the output, since a system with little human oversight can create risk nobody planned for. In fact, trends show an expectation for AI-related questions to show up in most new cyber policy applications within the next couple of years. - An AI vendor your business relies on can create a problem for you even if your own systems never get touched directly.
When Allianz surveyed thousands of risk managers worldwide for its 2026 Risk Barometer, AI jumped from the tenth biggest business risk all the way to second place in a single year, right behind cyber incidents themselves. That's the fastest single-year climb the survey has ever recorded, and it's a clear sign that insurers aren't the only ones paying closer attention to AI risk.
Companies that keep good records of their security habits, their employee training, and their AI usage policies tend to have an easier time at renewal. Evidence beats assurances now.
Here's a real Healthcare example: Cottage Health vs. Columbia Casualty.
- Cottage Health, a non-profit hospital, suffered two separate data breaches that exposed around 62,500 confidential medical records.
- When Cottage Health filed a claim, its insurer, Columbia Casualty, denied part of it. The insurer said Cottage Health hadn't kept up the security controls its policy required.
- Columbia Casualty also argued that Cottage Health hadn't answered its risk assessment questions accurately during the application process.
The case eventually settled, but it's still a widely cited reminder that a gap between what you promise on an application and what you actually do can cost you at the worst possible time.
finding the Best Cyber Insurance Provider
Choosing cyber insurance should start with a simple question: what would it really cost your business if something went wrong? Don't start with the price tag. Estimate what an outage, a recovery effort, or a fraud loss would actually cost first, then work backward from there.
-
Pick a provider that fits your industry. A healthcare company and a construction company don't face the same risks, and they don't face the same rules either.
-
Work with a broker who knows cyber insurance well. Because a good broker can spot exclusions and AI-related gaps in a policy before you're stuck living with them. Read your entire policy before you sign it.
-
Pay close attention to the waiting period. Check the deductible. Look closely at business interruption coverage and social engineering coverage. Watch for sublimits that could cap your payout lower than you'd expect, and watch for new AI-related exclusions that could leave a gap you didn't see coming.
-
Check the provider's financial strength and how their claims process actually works in practice, because a policy is only as good as the company's ability to pay when you need it.
Before you sit down with any insurance carrier, it's worth spending some time learning the basics on your own. Free resources like the Travelers Cyber Academy can help you walk into that conversation already knowing what to ask.
How Centre can help you
As part of Centre Technologies' security team, our specialists keep a close eye on how AI is reshaping the threat landscape. Our security assessments give you a clear picture of where your business actually stands and where the real gaps are. They'll help you set a real baseline for what "secure enough" looks like for your business, and support your planning for what happens if something does go wrong. These engagements include a business impact analysis and a risk assessment built around your actual environment, not a generic template.
Cyber insurance renewals are turning into evidence reviews, and Centre can help you walk in prepared. We help clients document the controls they already have. We confirm those controls actually meet compliance requirements. We help find the gaps worth fixing first, and we gather the technical proof insurers are increasingly asking for. That kind of preparation makes your entire security program stronger.
Here's how we can help you:
- Guidance on how to implement and integrate AI safely within your business
- Resources on preparing your systems from a cultural, operational, and financial standpoint
- Assistance in creating a strategy to stop attacks and/or minimize their impact including:
- Security awareness and anti-phishing training to users to recognize phishing, social engineering, and the new waves of AI-powered scams
- Real-time vulnerability scanning so problems are caught before an attacker finds them first
-
- Identification and prioritization of your network weaknesses for most effective patching and/or mitigation, making cost-effective use of security budgets
- Tools and/or services todetect and block connections to malicious parts of the Internet
- Creation or revision of your incident response or continuity plans
Don’t make the mistake of not having the proper tools or services to stop an infection before it evolves into a problem. The longer you wait, the greater the potential impact. Contact us to get started.
To learn more about how Managed Services can impact your business, check it our on the website.